
Continuous Compliance Across Your IT Ecosystem
Automate compliance across cloud, SaaS, DNS, DDoS, identity, and more—continuously validating controls, identifying gaps, guiding remediation, and keeping your organization audit ready.
Digitally map 20+ compliance frameworks to technical controls across your IT environment from one unified platform.

Turn Point-in-Time Compliance Into Continuous Compliance
Traditional compliance relies on periodic assessments, manual evidence collection, and weeks of preparation before an audit. But your IT environment changes every day—and so can your compliance posture.
CheckRed continuously maps compliance requirements to technical controls across cloud, SaaS, DNS, DDoS, identity, and other critical infrastructure, helping you identify gaps as they emerge, prioritize risk, guide remediation, and maintain audit-ready evidence.
With support for 20+ compliance frameworks, including SOC 2, ISO 27001, NIST, PCI DSS, HIPAA, CIS, and more, CheckRed helps you continuously validate your environment against the frameworks that matter to your organization.
Instead of asking whether you were compliant at your last assessment, know where you stand today.
Simplify Compliance Management with CheckRed
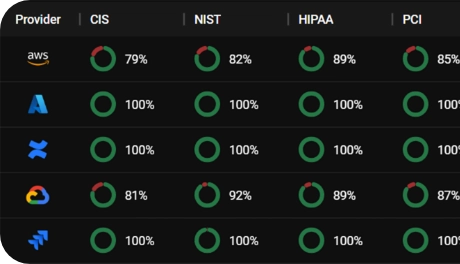
Automate Evidence Collection
Reduce manual screenshots, spreadsheets, and reporting with continuously collected compliance evidence across your entire IT environment.
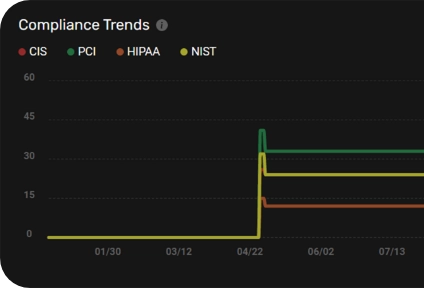
Continuously Validate Controls
Identify compliance gaps and configuration drift as your IT environment changes.
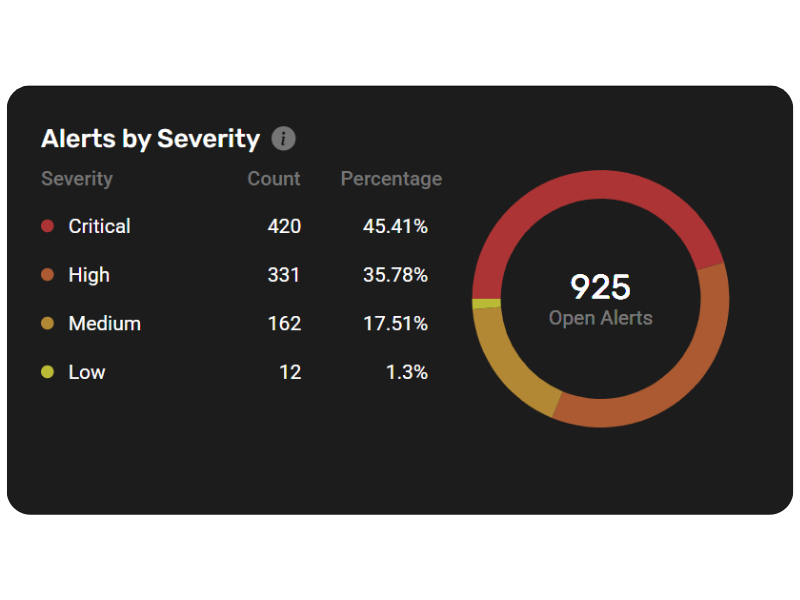
Prioritize What Matters
Cut through alert noise by prioritizing findings based on compliance and business risk.
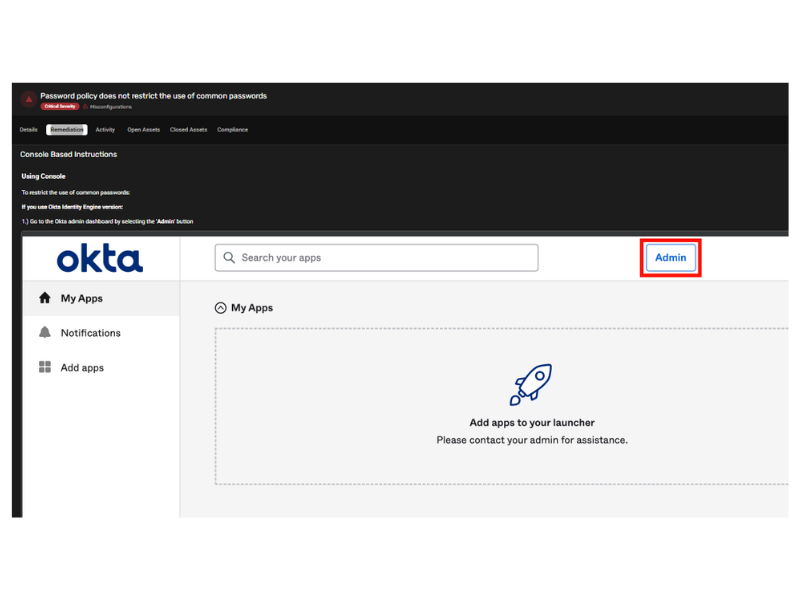
Remediate Faster
Give teams step-by-step guidance for every finding, helping them understand what needs to change and how to fix it.
The Business Impact of Continuous Compliance
Save Time
Automate discovery, monitoring, reporting, and guided remediation to reduce manual effort.
Stay Audit Ready
Continuously validate controls and maintain audit-ready evidence.
Reduce Costs
Lower compliance costs by automating audits, reducing manual work, and consolidating tools.
Reduce Risk
Identify and fix compliance gaps before they become security incidents.
Protect Your Reputation
Prevent compliance issues from impacting customer trust, business operations, and brand reputation.
Achieve Continuous Compliance with CheckRed
Start automating compliance for your cloud, SaaS, and DNS environments today. Reduce risks, prevent misconfigurations, and stay audit-ready with CheckRed.
Frequently Asked Questions
What is continuous compliance?
Continuous compliance is the ongoing monitoring and validation of security and compliance standards across cloud, SaaS, and DNS environments. Instead of relying on periodic audits, it helps organizations continuously align with regulatory requirements and internal policies through automated assessments, policy enforcement, and continuous alerting — ensuring environments remain secure, compliant, and audit-ready as they evolve.
How does continuous compliance differ from traditional compliance?
Traditional compliance typically relies on periodic assessments and scheduled audits, while continuous compliance provides ongoing monitoring, automated reporting, and continuous policy validation across cloud, SaaS, and DNS environments.
Instead of reviewing systems only at specific intervals, continuous compliance continuously evaluates configurations, tracks changes, and identifies compliance gaps as environments evolve. This approach helps organizations maintain stronger security posture, reduce audit preparation time, and stay consistently aligned with regulatory and internal policy requirements.
How does CheckRed support continuous compliance?
CheckRed supports continuous compliance by automating the assessment of cloud, SaaS, and DNS configurations against industry standards and regulations. CheckRed’s platform continuously monitors compliance with frameworks like ISO, GDPR, HIPAA, SOC 2, and DORA, identifying deviations and vulnerabilities. By providing continuous visibility and actionable insights, CheckRed enables organizations to maintain compliance effortlessly, ensuring that security policies are consistently enforced across all environments.
Subscribe to the Cybersecurity Breakdown
What attackers see. What security teams miss. Get monthly insights on DNS, SaaS, cloud, identity, compliance, and emerging cyber threats.