7 DNS Security Lessons from the CubePilot Hijacking
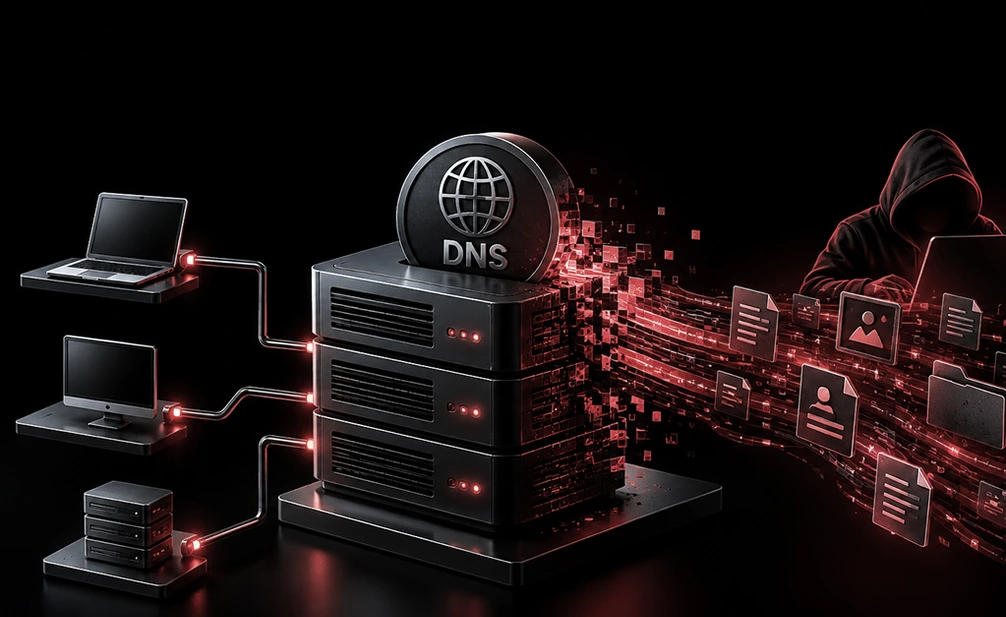
Executive Summary: The July 2026 DNS hijacking of drone technology company CubePilot demonstrates how control of DNS can become a direct pathway to traffic interception, credential exposure, and operational disruption. The incident is a reminder that DNS is not simply an infrastructure service—it is a security boundary. In this blog, we examine seven lessons security teams should take from the attack.
1. DNS Is an Attack Surface, Not Just a Network Service
DNS is often treated as background infrastructure: configure the records, make sure domains resolve, and move on. That mindset is increasingly dangerous. DNS determines where users and systems connect. When an attacker gains control over DNS records, they can influence that decision without necessarily compromising the application itself.
That is what made the CubePilot incident significant. According to reporting from BleepingComputer, an attacker gained control of the DNS settings for cubepilot.org on July 24, 2026, enabling traffic intended for CubePilot’s internal services to be redirected to attacker-controlled infrastructure. The security lesson is straightforward: anything that controls traffic deserves the same security scrutiny as the systems carrying the traffic.
2. A Valid HTTPS Connection Does Not Guarantee a Trusted Destination
One of the most important aspects of the CubePilot incident was the attacker’s acquisition of TLS certificates covering the company’s subdomains.
That creates an uncomfortable reality for users and defenders alike. HTTPS can confirm that a connection is encrypted and that the presented certificate is valid for a domain. It does not, by itself, prove that the DNS resolution behind that domain is still under the legitimate organization’s control.
CubePilot warned that credentials entered into its services on July 24—including its portal and forum—may have been captured. For security teams, this reinforces why certificate monitoring and DNS monitoring should not operate as isolated disciplines. They are interconnected components of digital trust.
3. DNS Changes Need Continuous Monitoring
Traditional security controls frequently focus on known vulnerabilities, endpoint activity, identity events, and network traffic. DNS configuration changes can fall between those operational boundaries. But an unauthorized change to an authoritative record can have an immediate impact.
Security teams should therefore be able to answer basic questions continuously:
- What DNS assets does the organization own?
- Which providers manage those assets?
- Who changed a record and what was changed?
- Was the change authorized?
- Does the resulting configuration introduce exposure?
CheckRed’s DNS Posture Management capabilities are designed around this visibility. The platform provides consolidated visibility across DNS providers, discovers DNS assets, identifies misconfigurations, and monitors DNS drift so teams can see who changed what and where. That changes DNS security from periodic review into continuous control.
4. Multi-Cloud DNS Makes Visibility Harder—and More Important
Enterprise DNS rarely lives in one place. Organizations may use Amazon Route 53, Azure DNS, Google Cloud DNS, Cloudflare, GoDaddy, or other providers simultaneously. That fragmentation creates an obvious governance challenge: security teams can struggle to maintain a complete picture of their DNS estate.
CheckRed addresses this through multi-cloud DNS visibility, bringing DNS zones, records, subdomains, and policy checks into a consolidated view across supported providers. The broader principle is important: you cannot secure what you cannot inventory.
A DNS security program should begin with comprehensive discovery and ownership mapping—not with an assumption that the security team already knows every active zone and record.
5. Misconfigurations Can Create the Conditions for a Bigger Attack
Not every DNS attack begins with a dramatic compromise. Sometimes, the underlying exposure is a configuration weakness that has existed unnoticed for months. Research has previously highlighted risks such as dangling CNAME records, where abandoned DNS records can potentially allow attackers to take over trusted subdomains.
This is why DNS posture management should go beyond detecting an active attack. Security teams need continuous assessment for conditions that make domain infrastructure easier to abuse. That includes identifying risky records, stale assets, unexpected configurations, and other forms of DNS drift before an attacker discovers them.
6. DNS Security Is Also About Business Continuity
The consequences of a DNS incident extend well beyond the DNS layer. Following the CubePilot incident, the company took multiple services offline as a precaution, including OEM services, its community forum, and documentation resources. It also advised customers not to flash firmware downloaded during the affected July 24–25 window until integrity checks could be completed.
This illustrates a critical point for CISOs: DNS compromise can become an availability, supply-chain, identity, and incident-response problem simultaneously. When trust in the routing layer is lost, organizations may have to suspend legitimate services while they determine what users may have accessed, what credentials may have been exposed, and whether distributed software or content can still be trusted. DNS resilience therefore belongs in business continuity and incident-response planning—not solely in network operations.
7. DNS Posture Should Be a Continuous Security Discipline
The CubePilot incident is a timely reminder that DNS is part of an organization’s external attack surface and should be managed accordingly.
A mature DNS security strategy should combine asset discovery, configuration assessment, change monitoring, misconfiguration detection, domain monitoring, and compliance validation. It should also connect DNS findings to the broader security posture rather than leaving them in a standalone infrastructure console.
This is where CheckRed’s DNS Posture Management approach becomes relevant. CheckRed provides centralized DNS visibility, automated asset discovery, misconfiguration detection, DNS drift monitoring, fake-domain detection, and continuous compliance capabilities across major DNS environments.
The objective is not simply to respond faster after a domain has been hijacked. It is to establish enough continuous visibility to identify weaknesses, unauthorized changes, and emerging exposure before they become an incident.
Treat DNS as Critical Security Infrastructure
The CubePilot incident shows why the security industry needs to stop treating DNS as plumbing. DNS sits at the intersection of identity, availability, application access, certificates, and user trust. When its control plane is compromised, the effects can propagate across all of those layers. The takeaway is that DNS deserves the same continuous governance applied to other critical security controls.
With CheckRed’s DNS Posture Management, organizations can consolidate DNS visibility, continuously identify misconfigurations, monitor configuration drift, discover assets, detect suspicious domains, and maintain compliance across complex DNS environments.